Sep 2026· Italian National Conference on Sensors· Vol 26· 0 citations· 19 references
Medicine
TL;DR
This study evaluates a calibrated two-tier detection pipeline combining an XGBoost gradient-boosted tree classifier for known-class prediction with a Monte Carlo dropout multilayer perceptron (MLP) as an independent uncertainty estimator, under conditions closer to real deployment than most prior evaluations.
Abstract
Closed-set evaluation is the most common method in Internet of Things (IoT) sensor network botnet attack detection research. In this setting, classifiers are tested only on attack families encountered during training. As a result, they often fail to detect genuinely new (zero-day) malware in real-world environments. This study evaluates a calibrated two-tier detection pipeline combining an XGBoost gradient-boosted tree classifier for known-class prediction with a Monte Carlo (MC) dropout multilayer perceptron (MLP) as an independent uncertainty estimator, under conditions closer to real deployment than most prior evaluations. The uncertainty model is used to flag unfamiliar traffic that may represent zero-day traffic. The classifier is trained and calibrated on the Bot-IoT dataset and evaluated for zero-day generalization on N-BaIoT, which contains the previously unseen Mirai and BASHLITE malware families. During data preparation, a severe train/test duplication problem was identified. Around 97% of a naive split was found to be duplicates and was removed before splitting. The base classifier achieved 99.4% accuracy in known-class detection. However, the confidence scores were negatively correlated with zero-day traffic, producing an area under the receiver operating characteristic curve (AUROC) of 0.32. This indicates the overconfident misclassification of unseen attacks. The proposed uncertainty gate improved zero-day discrimination to an AUROC of 0.66, with catch rates reaching 13.75% for Mirai. An explainable AI analysis using Shapley Additive Explanations (SHAP) linked this gap to packet size statistics. To evaluate practical feasibility, the complete framework was deployed on an embedded Raspberry Pi Compute Module 5 (CM5) edge device. The full uncertainty-gated pipeline achieved mean inference latency of 15.03 ms per sample. Overall, these findings demonstrate that uncertainty-aware gating can improve zero-day robustness over conventional closed-set classification in resource-constrained IoT sensing environments.
Internet of Things (IoT) intrusion detection on a gateway has to handle three coupled risks: heterogeneous device traffic distributions, unknown attack families arriving at inference time, and softmax confidence that does not separate correct predictions from confident errors on novel traffic. We present DA-DCC-IDS, a...
This work contributes a comparative evaluation of lightweight detection models, consistent attention to security-critical metrics, and interpretable insights to support practical cybersecurity deployment.
Nwagbara Chisom Telvin, Gilbert Imuetin Osaze Aimufua, Raymond Ternenge Igbudu· FUDMA Journal of Sciences· 0 citations
The expansion of the Internet of Things (IoT) has intensified cyber risk in Edge deployments with limited computational resources, where conventional intrusion detection systems are unfeasible. Aiming to reduce this gap, a lightweight anomaly detection system for IoT networks has been designed and implemented, structur...
Fernando Gutiérrez-Portela, Oscar Augusto Diaz Triana, A. Yule et al.· Future Internet· 0 citations
Federated learning (FL) is a promising approach for IoT intrusion detection because it enables distributed clients to collaboratively train models without pooling raw network-flow records. However, IoT traffic is often heterogeneous across monitoring sites, devices, and attack scenarios, which can degrade federated mod...
Hassan A. Shafei· 2026 IEEE 1st International...· 0 citations
The rapid growth of Internet of Things (IoT) deployment has increased exposure to Distributed Denial of Service (DDoS) attacks, while the latency and bandwidth costs of cloud-centric intrusion detection constrain real-time response. This paper presents a fog-based DDoS detection framework that combines XGBoost with inf...
Abeer Albalawi, Linda Mohaisen· Italian National Conference...· 0 citations
This work shows that production‐grade, privacy‐preserving intrusion detection is feasible in IoT networks at the edge, and addresses the concerns of data privacy and non‐IID data distribution inherent to distributed IoT networks.
Vaibhav Joshi, Abishi Chowdhury, Amrit Pal et al.· Software, Practice & Experie...· 0 citations
Related blog posts
MIT News · Artificial Intelligence· news.mit.eduOct 8, 2026
Jennifer Neville did not want to go into computer science—but that’s exactly where she landed. Neville discusses the starts and stops that led to her professional sweet spot and her work identifying “surprising failures” making it hard for AI to handle complexity. The post What AI gets wrong and what failure teaches us appeared first on Microsoft Research.
Microsoft Research Blog· microsoft.comSep 29, 2026
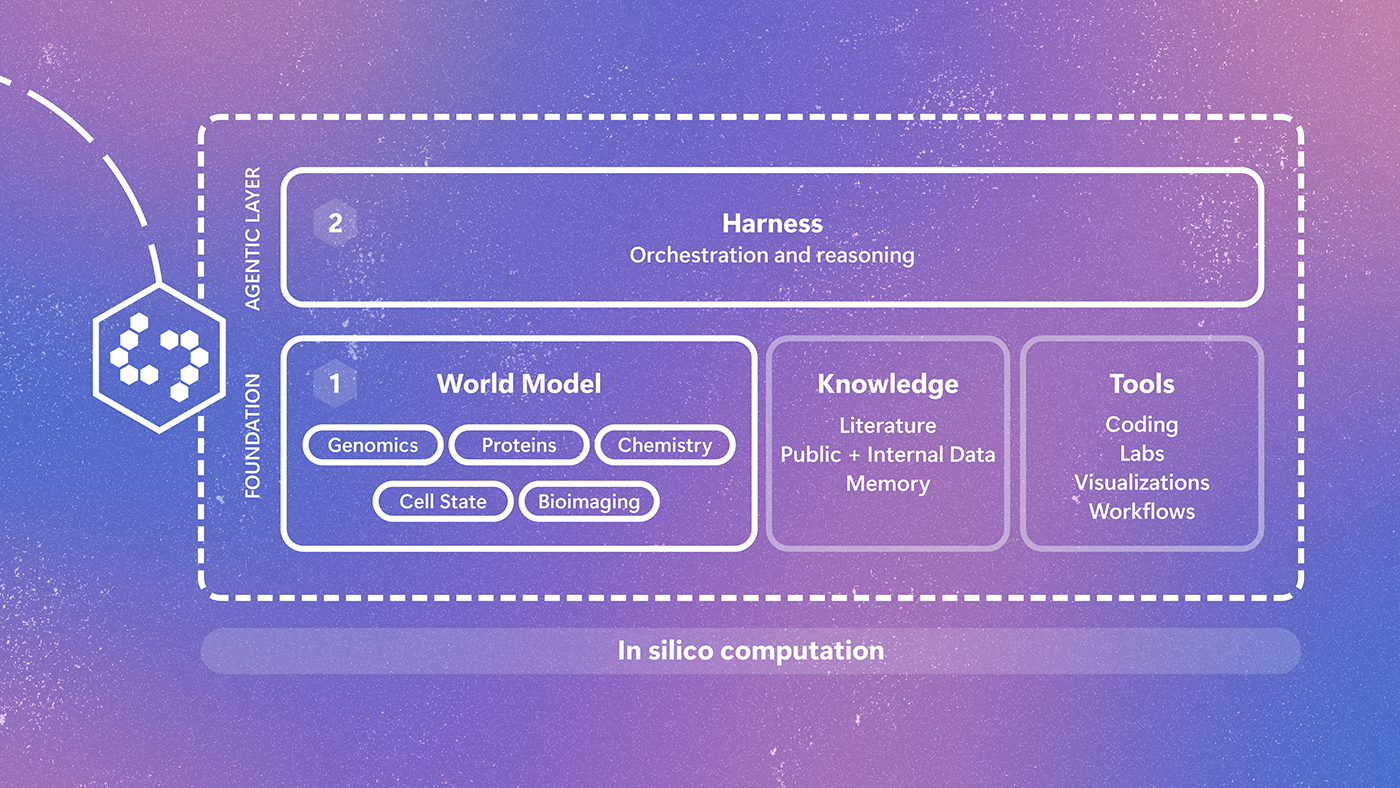
Biology doesn't operate in silos, and neither should the AI representation of it. Quine is an early-stage research effort to create a multimodal world model of biology. By connecting insights across biological scales and modalities, Quine helps scientists computationally search a space far larger than intuition allows and prioritize hypotheses before they reach the lab. Experimental results provide important feedback, helping researchers sharpen future research directions. The post Introducing Q…
We use cookies to run the site and, with your consent, for analytics and to show ads.
See our Cookie Policy.