Skip to content

Temporal Generalization and Explanation Stability of Control Flow Graph Neural Networks for Malware Detection

Sep 2026 · arXiv.org · Vol abs/2609.24280 · 0 citations · 71 references
Computer Science

TL;DR

A strict temporal split is addressed with every model trained on one period and scored once on a later one, which results in results about robustness to distribution shift, not malware evolution.

Abstract

Malware detection is a critical task in cybersecurity, and graph neural networks over control flow graphs have shown promising results for it. However, detectors are usually evaluated on a random split of a corpus collected over a single period, which cannot show how well a model generalizes to later samples. This study addresses that limitation with a strict temporal split: every model is trained on one period and scored once on a later one. Two corpora of control flow graphs, each node carrying 37 features, were extracted statically from 1,989 Windows portable executables: 459 graphs from 2024-2025 for training and 223 from 2026 for evaluation. Twelve variants and a flat-feature control were trained on the earlier corpus. The choice of message-passing operator changes robustness to the shift significantly, and every pairwise gap that survives correction separates an aggregating architecture from one built around a learned attentional readout. The ranking also reverses: the flat control, which sees node features but no topology, is the best in-distribution model and among the worst across the boundary, so a conventional benchmark would have rejected message passing. Neither recalibration nor ensembling substitutes for the operator choice. Attributions do not shift, but explanation validity is architecture-specific, and the most accurate operator on the later corpus is the hardest to explain. An architecture derived from the finding matches the best searched operator without search. The shift affects both malware and benign classes alike, so these are results about robustness to distribution shift, not malware evolution.

View source

Similar papers

Sep 2026

A hybrid graph- and sequence-based deep learning framework for behavioral analysis of metamorphic malware

This paper investigates a unified behavioral analysis framework that combines temporal and structural representations of Windows API call sequences: a sequential view based on learned API n-gram representations and a Bidirectional LSTM (BiLSTM) encoder, a structural view derived from the API transition graph, and a mul...

Parisa Golabvand, N. Mikaeilvand, Abbas Mirzaei et al. · 0 citations
Open access Sep 2026

Graph Neural Networks with Code Structure Embeddings for Model-Agnostic Multi-Class Detection of AI-Generated Programs

GraphCSE, a detector for unseen generators of AI-generated code, represents a program as a heterogeneous code graph with four edge relations and fuses structural and semantic node channels through a learned per-node gate before relation-aware graph attention, restoring model-agnostic detection.

Dr.Hayder Kareem Algabri · 0 citations
Sep 2026

Stress-Testing Structure-Aware Calibration of Malware Graph Neural Networks under Type Shift

Post-hoc malware calibrators can condition confidence on graph structure, but their structural inputs may leave the support represented by validation data under malware-type shift. We study this risk on MalNet-Tiny by holding out each of four malware types across three seeds, freezing a graph isomorphism network, and f...

Jun-Ru Zhu, Yi-Xin Yang, Xiao-Qing Ding et al. · 0 citations
Open access 2026

MalBERT-Temporal: Transformer-Based Zero-Day Malware Detection in Windows Executable Binaries Under Strict Temporal Isolation

A Transformer-based malware detection approach named MalBERT-Temporal that reshapes the 2,381-dimensional BODMAS PE feature vector into 16 contiguous feature-group tokens and then processes these tokens with Transformer encoder layers employing multi-head self-attention to model interactions among all tokens is introdu...

Manar Alanazi, Israa Alsiyat · 0 citations

Related blog posts

Microsoft Research Blog Nov 3, 2026

Learn the rules: The hacker mindset

Research Manager Mike Walker reflects on a career spanning hacker culture, cybersecurity, and AI, sharing lessons about trust, teamwork, leadership, and why solving difficult problems requires curiosity, judgment, agility—and an understanding of the rules. The post Learn the rules: The hacker mindset appeared first on Microsoft Research.

MIT News · Artificial Intelligence Sep 29, 2026

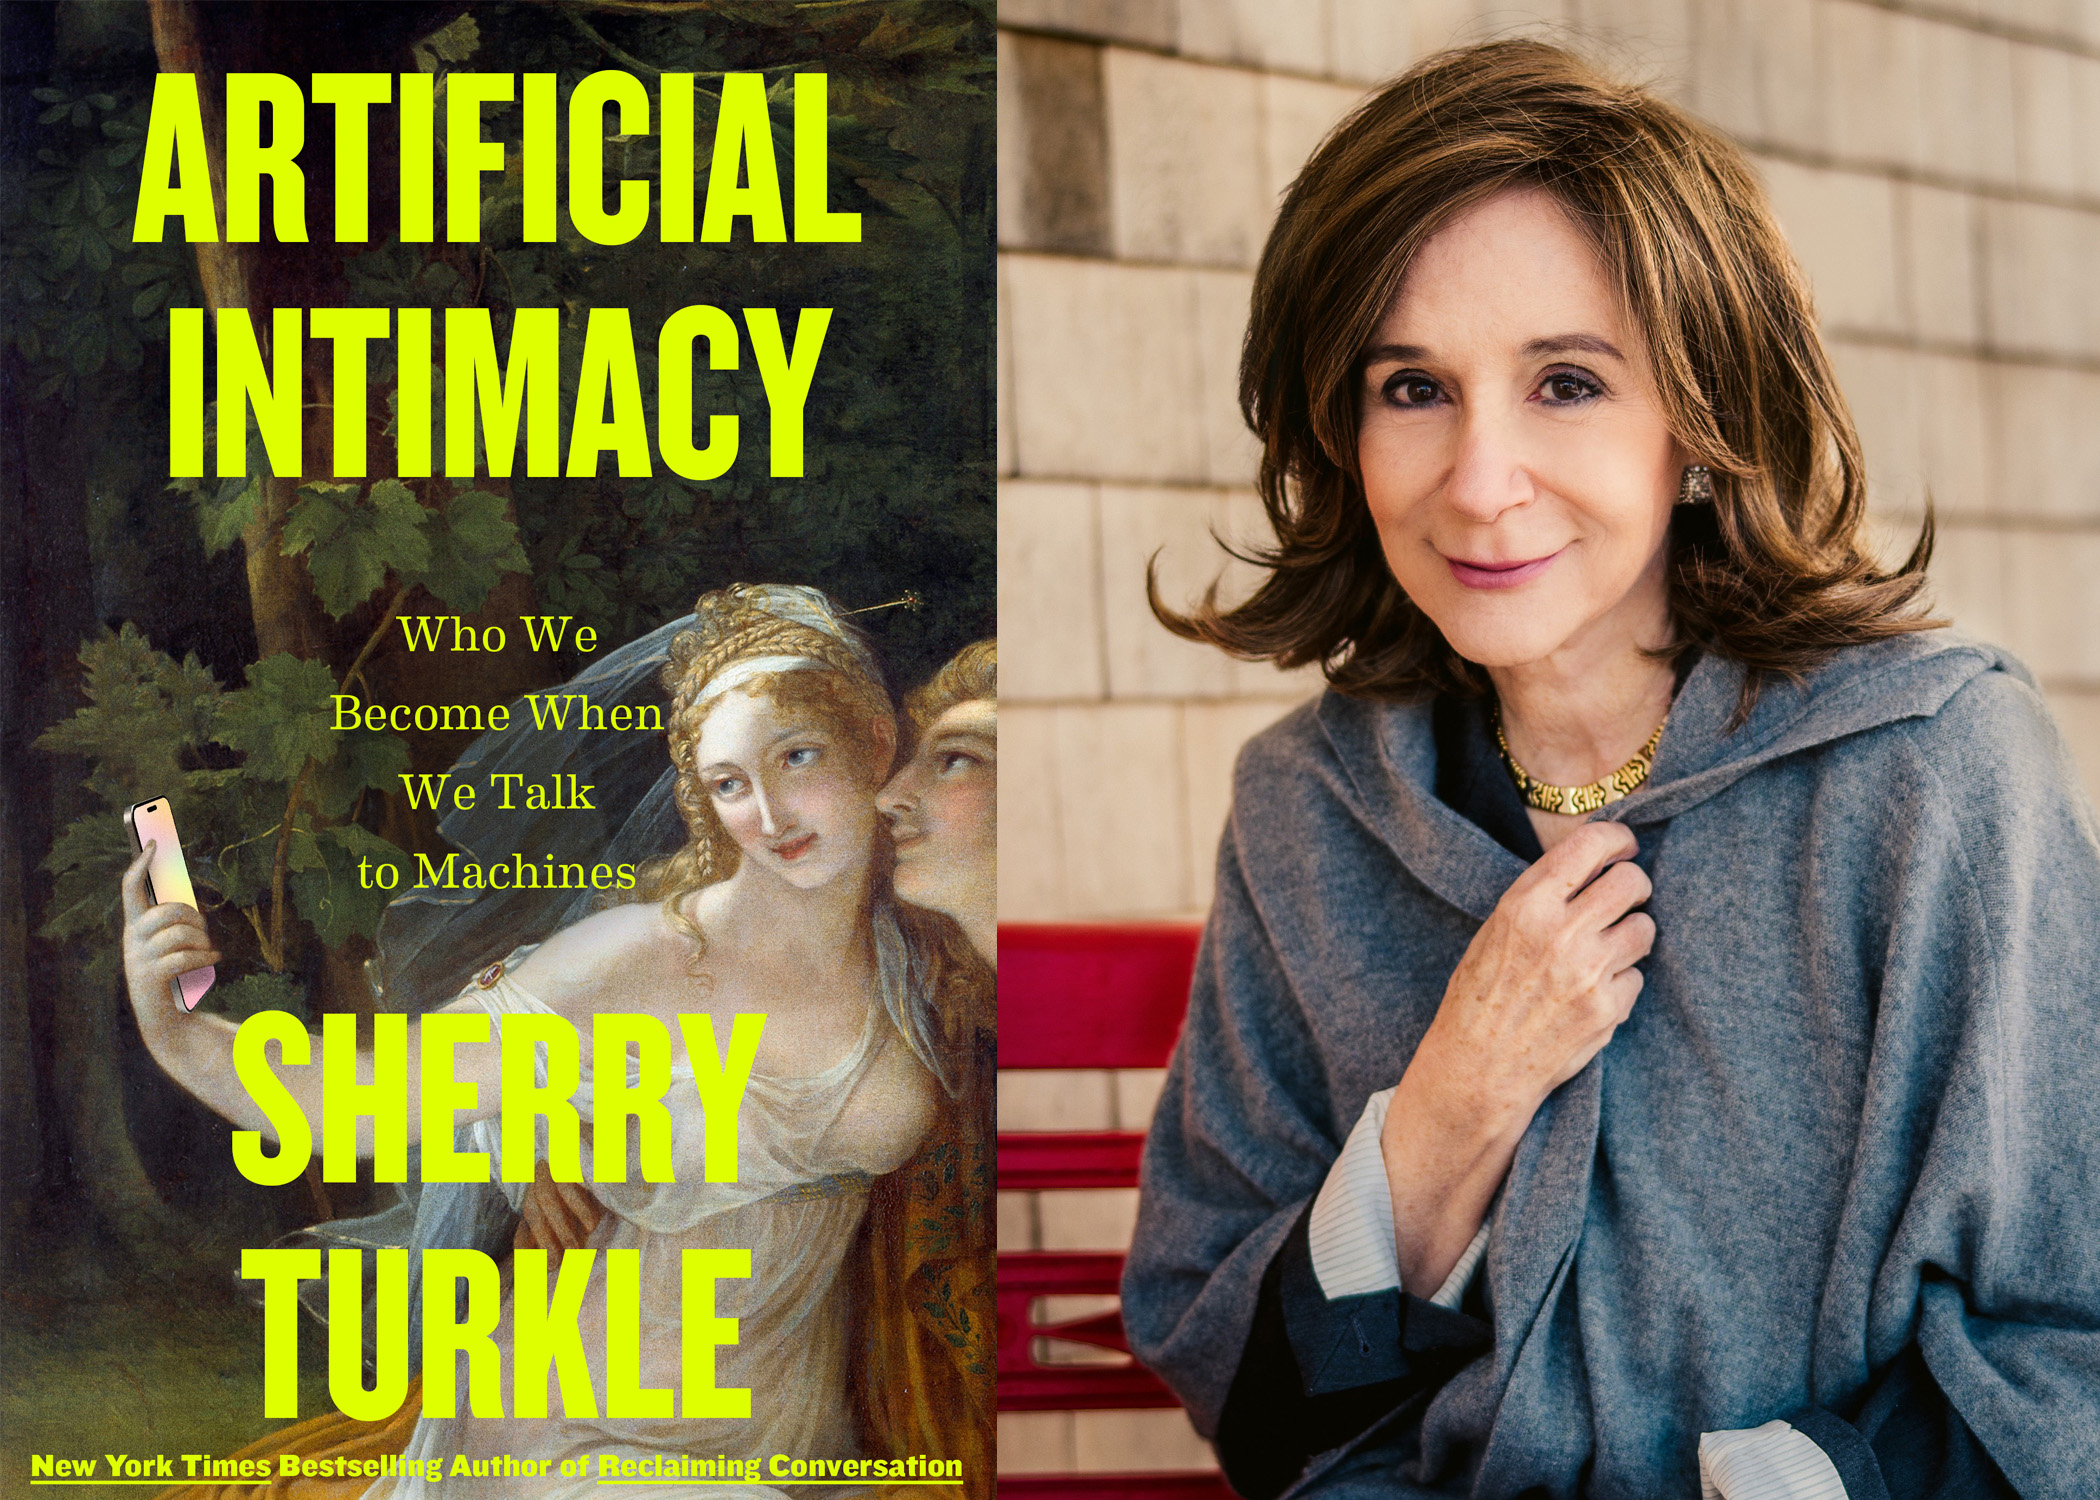
Who we become when we talk to machines

Professor Sherry Turkle’s new book, “Artificial Intimacy,” offers a withering critique of chatbots and the antisocial dynamics she believes they encourage.

We use cookies to run the site and, with your consent, for analytics and to show ads. See our Cookie Policy.