Sep 2026· American Journal of Data Science and Artificial Intelligence· 0 citations· 49 references
TL;DR
The findings demonstrate the effectiveness of the graph-based methods in providing high-quality behavioral dependencies, with better accuracy and fewer false alarms and greater explainability in real-life insider risk monitoring.
Abstract
The insider threat is still among the most difficult cybersecurity risks because of the access and capabilities of insiders to hide malicious or careless actions in the ordinary operations. The rules-based system, statistical anomaly detection and traditional machine learning tools are not always efficient in identifying the relational and contextual dependence in an enterprise setting which limits predictive capability as well as high false-positive. This paper presents a graph-baseds model of active preemptive insider threat detection. The Insider Threat Dataset of Multi-source behavioral logs of Classified Environments are converted to a heterogeneous interaction graph, where the nodes represent users, devices, and resources, and the edges indicate the frequency of interaction, sensitivity, and time patterns. Normative measures such as degree, between, eigenvector centrality, community membership, motif patterns and PageRank are derived to display aberrant relational activity. Empirical analysis has shown that a higher number of off-hours of printing/burning, larger volumes of data being exfiltrated, longer occupancy duration, and high-risk travel occur in malicious insiders occupying more influential network positions (much higher PageRank). The full prediction accuracy (FNNs classify every sample correctly) of Graph Neural Networks (GNNs) is high (F1 = 1.0, AUC = 1.0), which is significantly higher than that of the traditional baselines (Random Forest: F1 = 0.7576; XGBoost: F1 = 0.6753). The findings demonstrate the effectiveness of the graph-based methods in providing high-quality behavioral dependencies, with better accuracy and fewer false alarms and greater explainability in real-life insider risk monitoring.
Enterprises today face serious risks from insider employees whose malicious activities can cause heavy financial and reputational damage. Traditional insider threat detection methods mostly highlight abnormal users or abnormal time periods (like a day or a week). However, in practice, a single user may generate thousan...
D. N. Kumar, Kalpana K· International Conference on...· 0 citations
Detection of insiders is challenging due to potential abuses of authorised access. In this work, a privacy-preserving approach to the analysis of enterprise event logs leveraging behavioural attributes, graph-based relations between user activities, anomaly detection and federated learning is proposed. The proxy target...
A. Rakshan, F. George, Ashok Immanuel V· International Conference Com...· 0 citations
Many organizations face increasing risk from the insider threats where employees misuse the legitimate access to compromise sensitive data or systems. It is often complex in detecting the using the traditional ways. To address this issue, CausalXBoost framework was proposed which is detects the malicious behavior with...
Vaishnavi Jayaraman, Harvin Krishnan H, Vishaal Rgs et al.· International Conference Com...· 0 citations
Insider threats remain one of the most complex and damaging security challenges in modern
organizations. While much research has focused on identifying malicious insiders, there is limited
understanding of benign insider behaviors that may unintentionally compromise organizational
security. This study introduces a n...
Ndukuba Peter Chimampka· International Journal of Com...· 0 citations
EdgeGuard, a deployed cyber-threat knowledge graph that merges eleven public threat feeds into one Neo4j database via MISP and the STIX 2.1 exchange format, is measured, showing that half of the vulnerabilities known to have been exploited were listed as exploited within five days of their publication, and that a large...
Kalin Kopanov, K. Dineva, Ivaylo Keremidarski et al.· Information· 0 citations
This project asks whether feeding a report into a knowledge-graph retrieval system, Microsoft GraphRAG, rather than a standard vector-similarity retrieval system (Naive RAG), produces detection plans that rely more on these durable, top-of-pyramid clues.
A. Kabra, Prakhar Paliwal, M. Hanawal· 0 citations
Related blog posts
MIT News · Artificial Intelligence· news.mit.eduOct 13, 2026
Machine-learning networks can learn without detailed instructions from a designer. Those that do may offer insight into how the brain reorganizes itself during learning.
MIT News · Artificial Intelligence· news.mit.eduJul 15, 2026
Assistant Professor Pat Pataranutaporn describes a new interface that lets everyday users glimpse inside an AI's neural network before their chatbot ever says a word.
Microsoft Research Blog· microsoft.comJul 13, 2026
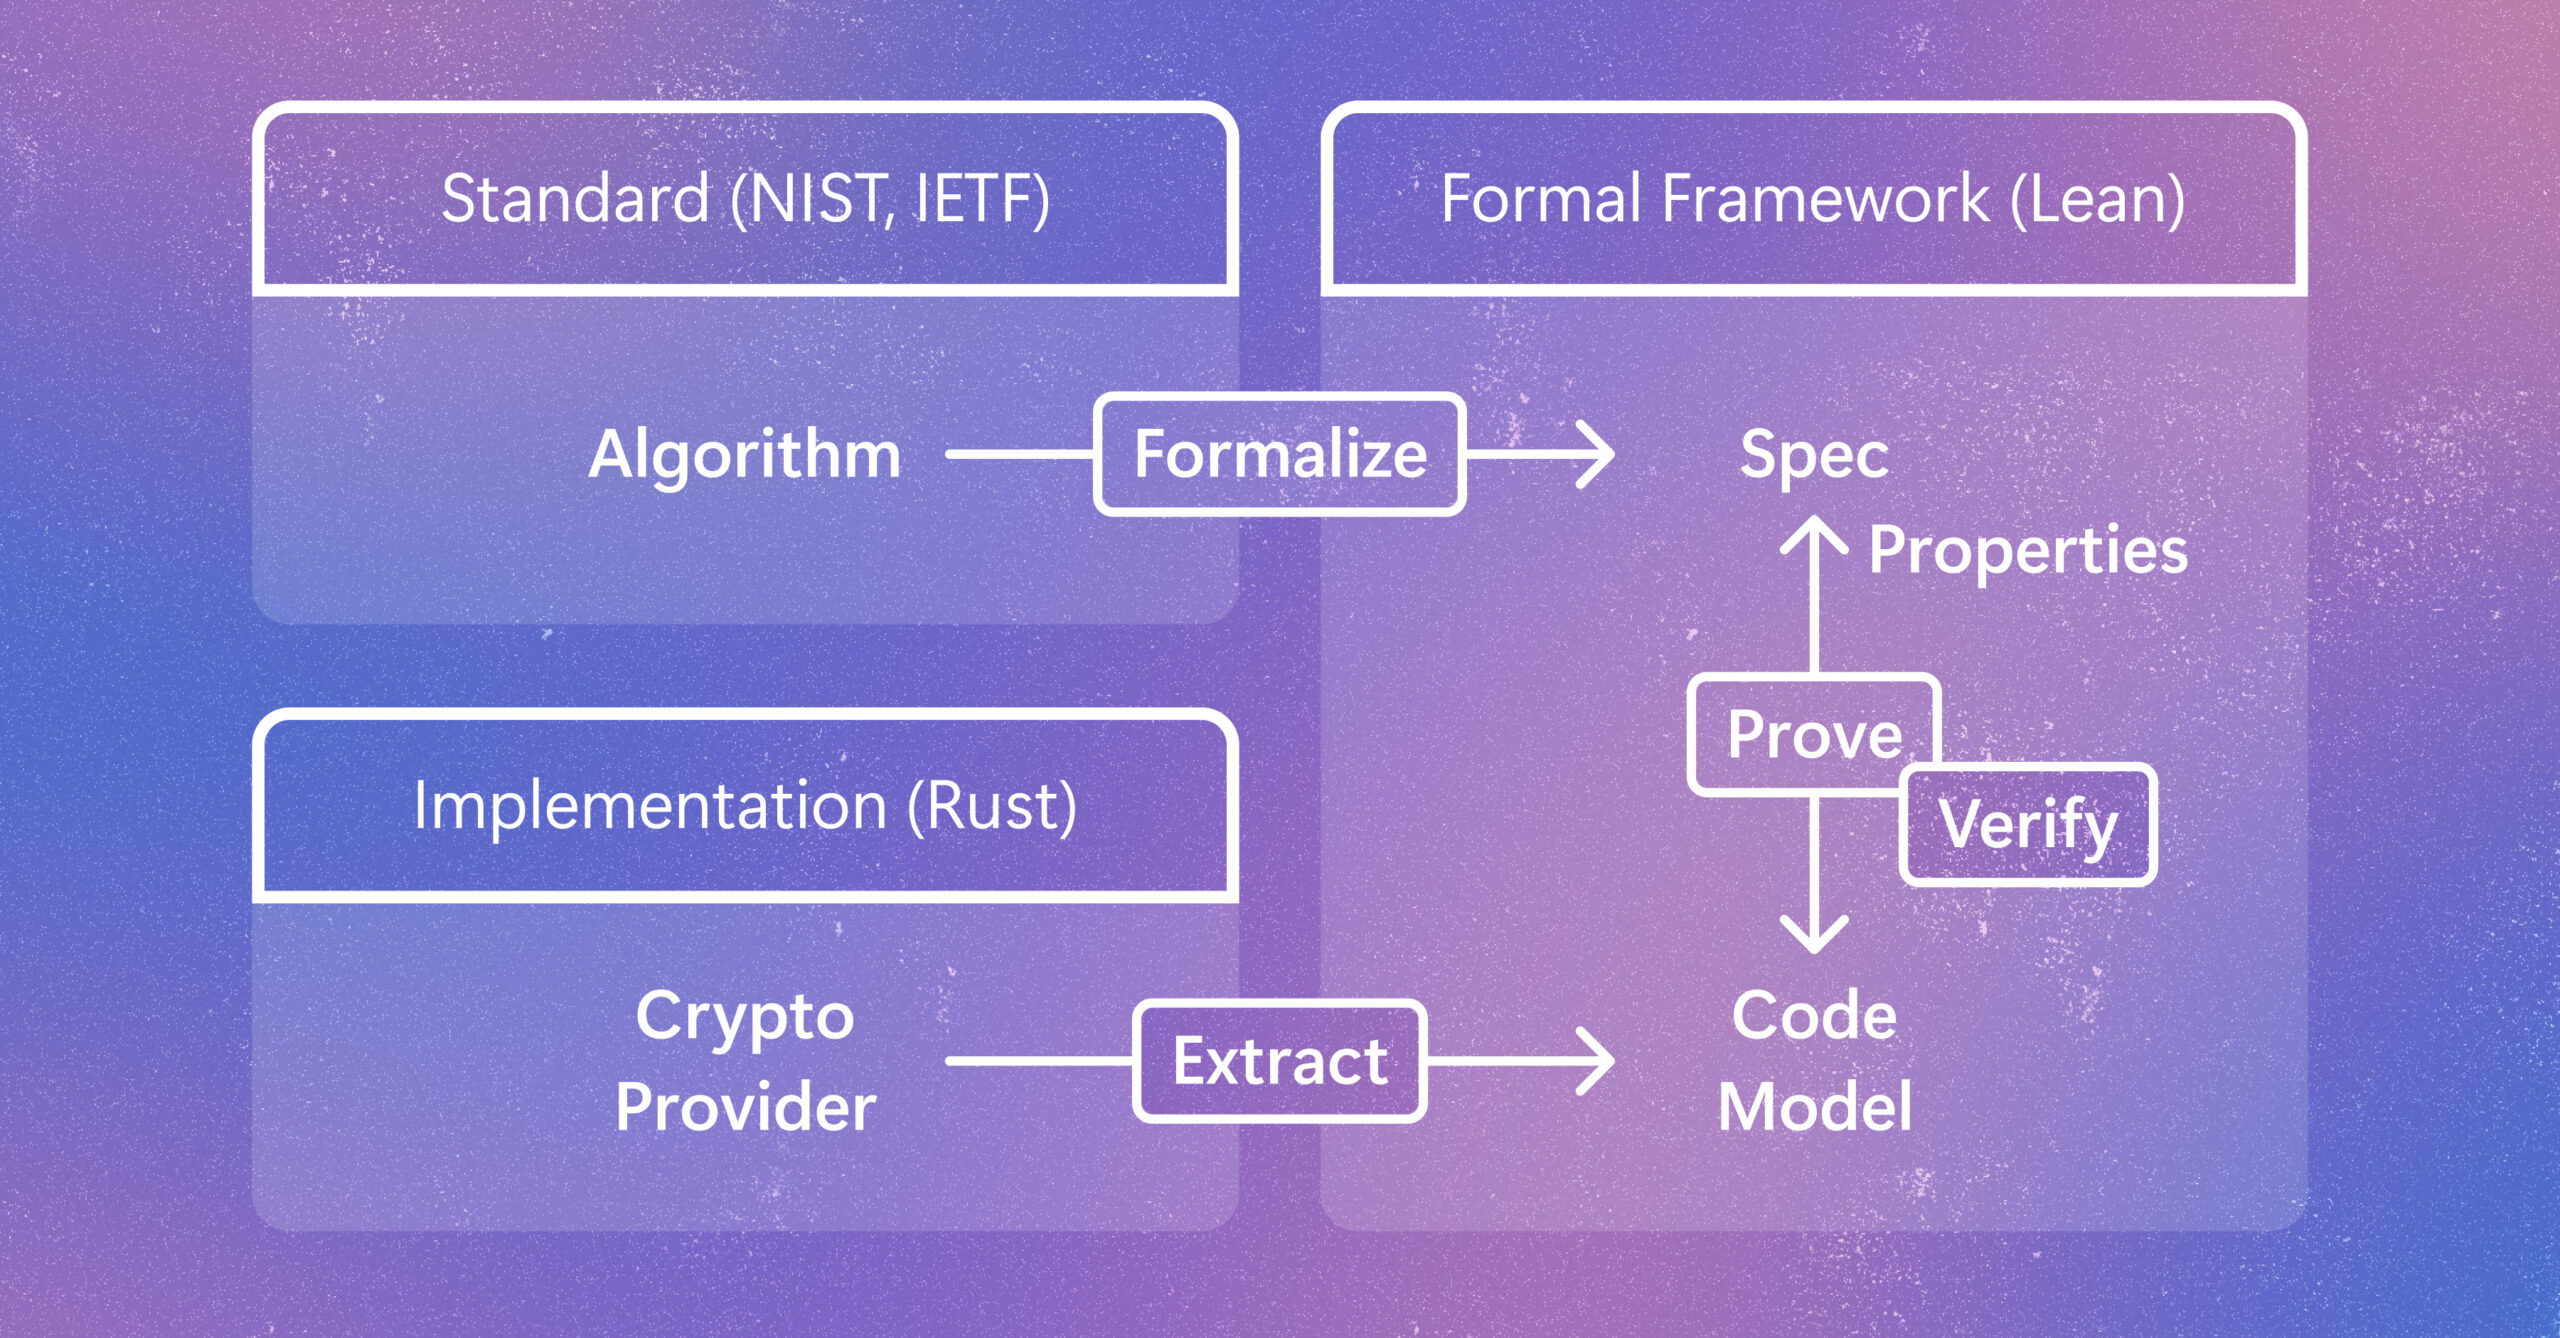
Cryptographic code supports vital protections in modern computing systems. Learn how a new method helps verify code as developers write it while preserving speed and adaptability as it gets implemented and evolves. The post Verifying Rust cryptography in SymCrypt, from standards to code appeared first on Microsoft Research.
MIT News · Artificial Intelligence· news.mit.eduJul 6, 2026
PhD student Rachel Sava, winner of the Envisioning the Future of Computing Prize, explores transformative improvements and dystopian risks of neural technology.
We use cookies to run the site and, with your consent, for analytics and to show ads.
See our Cookie Policy.