A Robust watErMArk-based fingeRprint frameworK for GNNs, named REMARK, which first generates carefully crafted in-distribution watermark graphs that maximize output differences between GNN models, thus mitigating OOD-induced performance degradation.
Abstract
The high training cost of Graph Neural Networks (GNNs) has raised growing concerns regarding model ownership infringement, such as model stealing and unauthorized misuse. To verify model ownership and prevent significant economic losses, two groups of GNN Ownership Verification (OV) methods have been proposed: watermark-based methods and fingerprint-based methods. However, these methods typically face three limitations: (1) the performance degradation of protected models caused by out-of-distribution (OOD) watermark graphs with respect to the training set; (2) the unrealistic assumption that surrogate models have been trained on a watermark-containing training set; and (3) over-reliance on specific output levels for fingerprint extraction. In this paper, we propose a Robust watErMArk-based fingeRprint frameworK for GNNs, named REMARK. REMARK first generates carefully crafted in-distribution watermark graphs that maximize output differences between GNN models, thus mitigating OOD-induced performance degradation. REMARK then extracts robust fingerprints from these output differences to verify GNN ownership, thereby removing the assumptions that surrogate models must be trained on a watermark-containing dataset or expose specific output levels. Extensive experiments across widely used real-world datasets and GNN architectures demonstrate that REMARK achieves state-of-the-art OV accuracy and robustness while preserving the utility of protected models.
This work proposes a novel lattice quantization-based backdoor watermarking framework for DNNs in black-box settings that embeds the owner’s identity into trigger samples via lattice quantization index modulation, achieving identity encoding while maintaining trigger imperceptibility.
Model watermarking is a commonly used ownership verification technique for protecting the copyright of deep learning models. However, in practically deployed black-box model service scenarios, existing methods typically rely on misclassification-based backdoor trigger mechanisms, or assume that the verifier can obtain...
Jing Xiao, Song Xiao, Chao Guo et al.· Journal of King Saud Univers...· 0 citations
Image watermarking supports provenance and attribution by embedding verifiable identity information into images. Practical deployments, however, must jointly satisfy requirements for attack resistance, false-positive rate (FPR), image quality, and latency. Existing watermarking methods are robust to different classes o...
Mingzhe Li, Yue-Feng Peng, Kejing Xia et al.· 0 citations
Results show that the copy–paste attack degrades watermark detectability when using very sparingly and only short sentences are used, while deletion becomes effective only at extreme levels on short texts, and underscore the need for future watermark designs to prioritise resilience to semantic and cross-lingual transf...
Jakob Elias Albrecht, A. Jakoby, Benno Maria et al.· 0 citations
This paper upgrades fingerprint evidence from a source-boundary transferability heuristic to an explicit ownership-separation objective, formulate fingerprint construction as a decision difference region (DDR) search problem and solve it with two non-invasive variants, giving owners a tunable trade-off between construc...
Tian-Xiang Luo, Zi Yang, Xiao-Rui Dai et al.· Applied intelligence (Boston...· 0 citations
To comply with recent regulations requiring traceable generated content, modern watermarking has adopted multi-bit post-hoc watermarking schemes. These modern designs rest on an encoder-decoder pair implemented as deep neural networks. These models are usually treated as pure black-boxes trained end-to-end, with the no...
Enoal Gesny, Eva Giboulot· 0 citations
Related blog posts
MIT News · Artificial Intelligence· news.mit.eduOct 13, 2026
Machine-learning networks can learn without detailed instructions from a designer. Those that do may offer insight into how the brain reorganizes itself during learning.
Microsoft Research Blog· microsoft.comJul 13, 2026
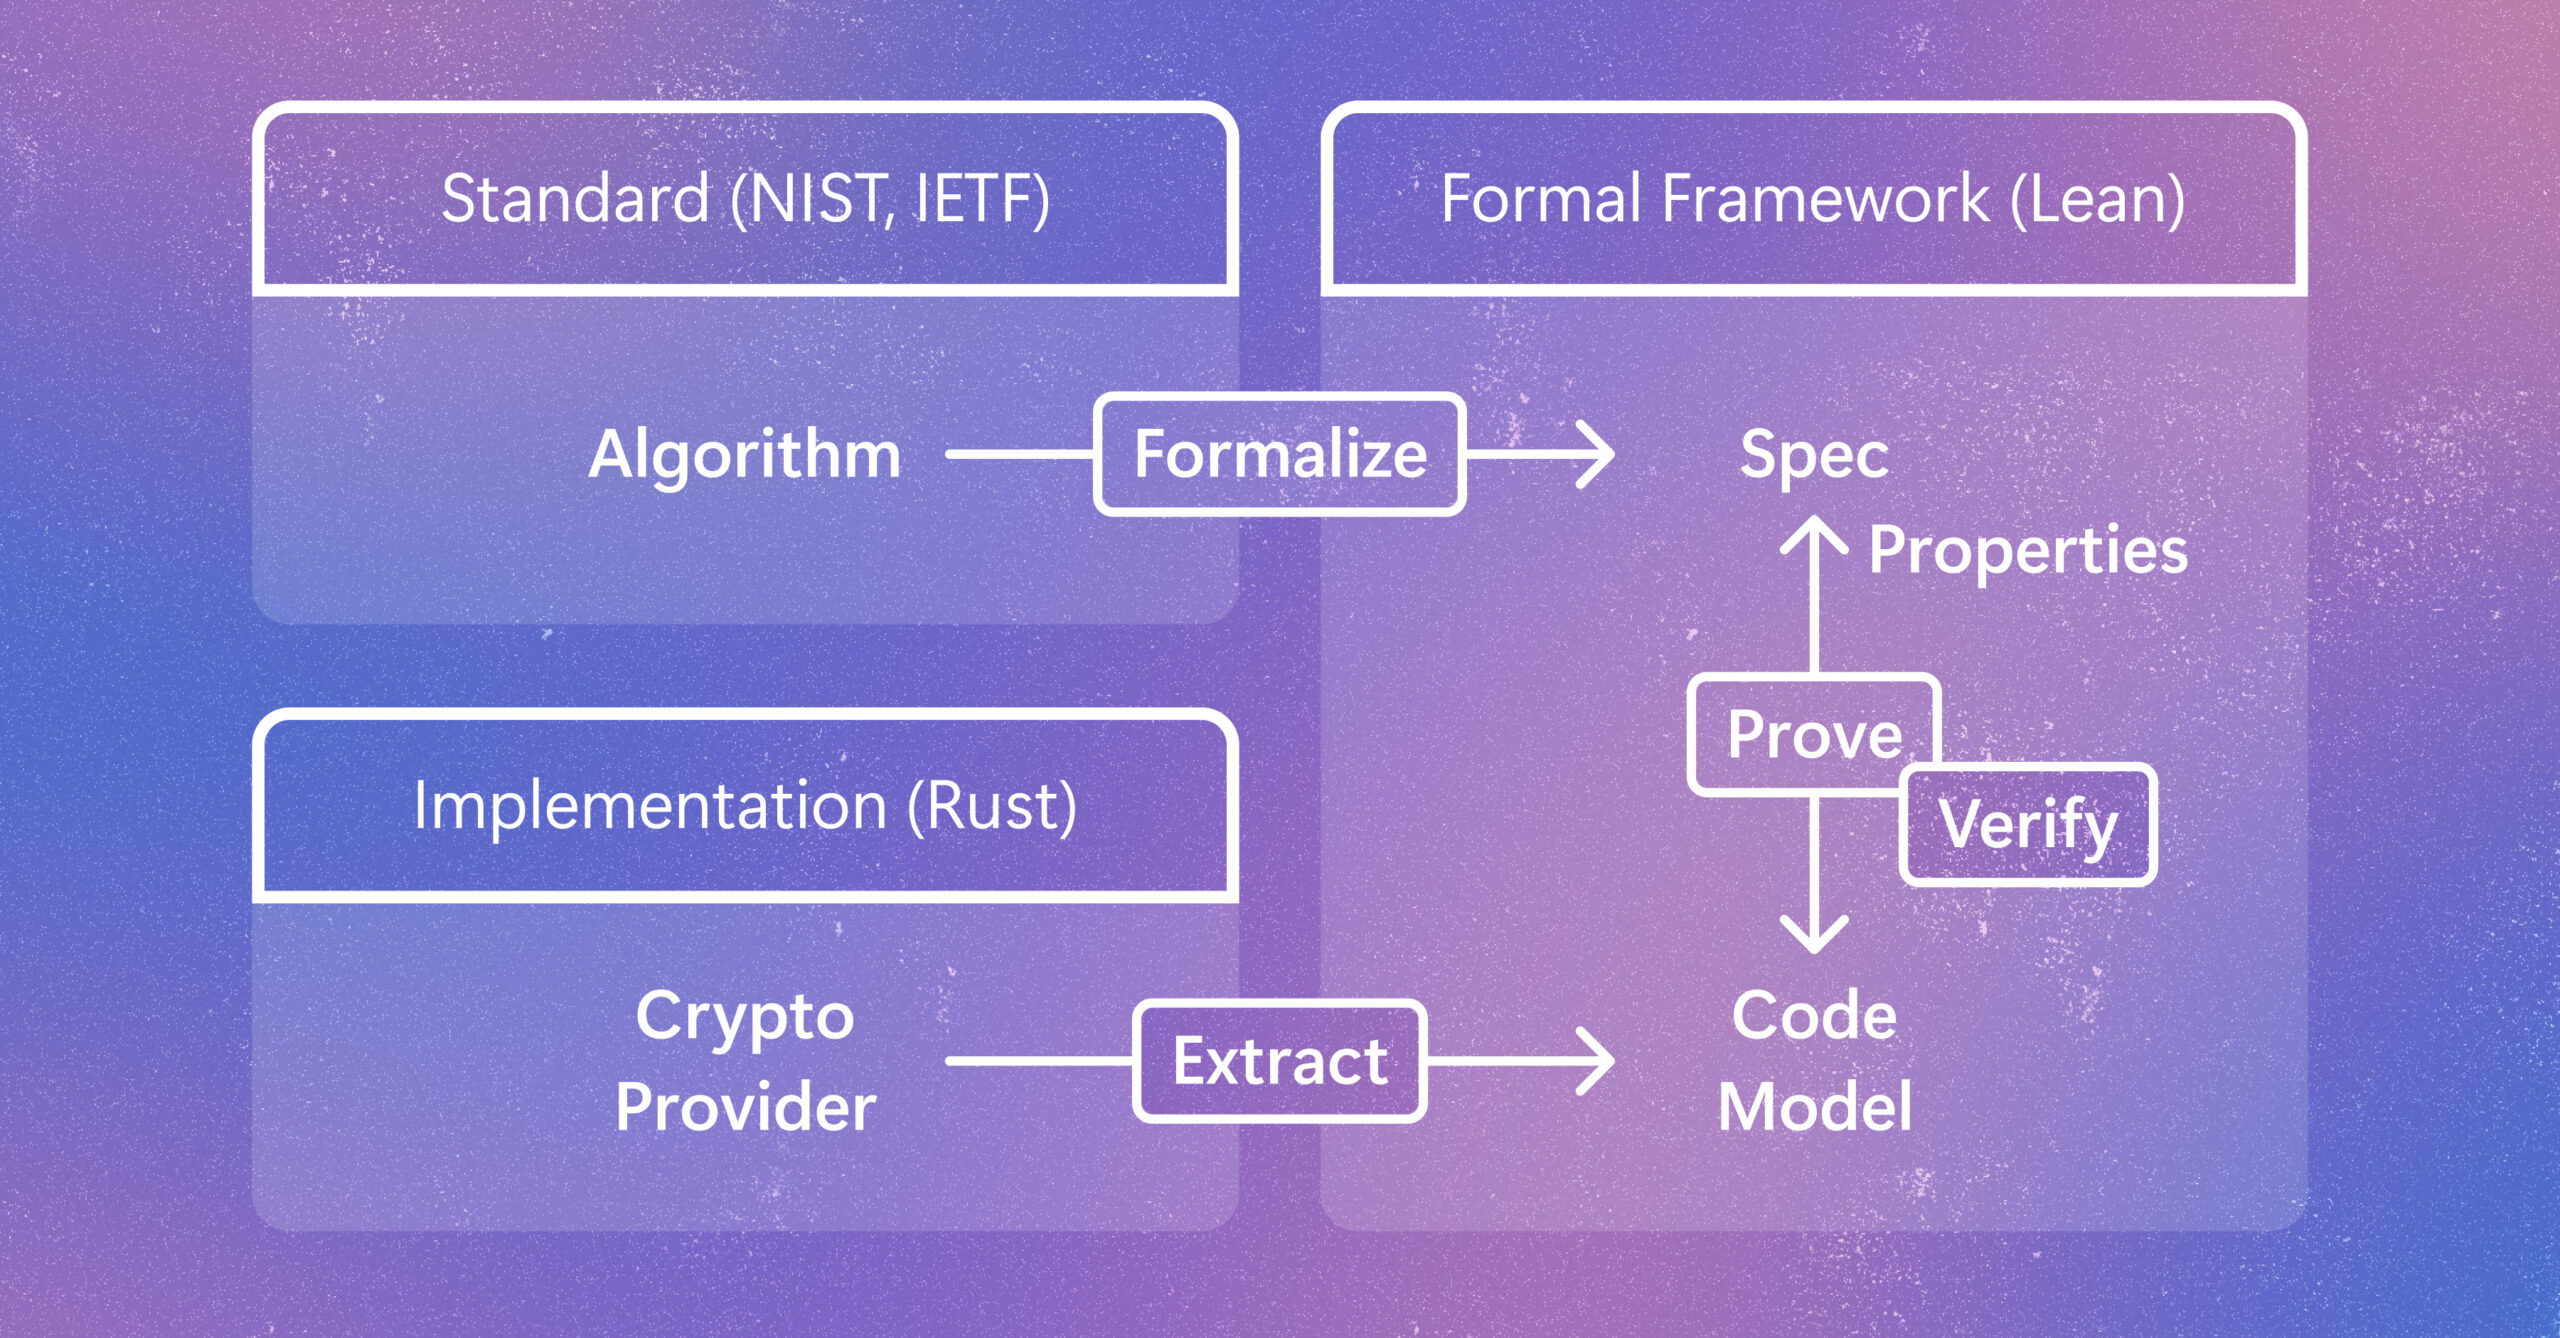
Cryptographic code supports vital protections in modern computing systems. Learn how a new method helps verify code as developers write it while preserving speed and adaptability as it gets implemented and evolves. The post Verifying Rust cryptography in SymCrypt, from standards to code appeared first on Microsoft Research.