Skip to content

A Behavioral Swarm Intelligence Framework with a Hybrid 1D-CNN for Identifying Zero-Day Attacks in Kubernetes-Driven Hybrid Clouds

Aug 2026 · Basrah journal of science · 0 citations

TL;DR

C Cerberus, a hybrid detection framework that integrates, in a unique manner, a container-level behavioral analysis running a lightweight one-dimensional convolutional neural network and a collective level of analysis based on behavioral swarm intelligence, demonstrates that it can be applied in practical cloud-native scenario.

Abstract

Zero-day exploitation in hybrid clouds based on Kubernetes is difficult to detect, as traditional signature detection systems and standalone anomaly detection models are running out of context and are prone to generating numerous false positives in dynamic workloads. In this paper, we bridge this gap with Cerberus, a hybrid detection framework that integrates, in a unique manner, a container-level behavioral analysis running a lightweight one-dimensional convolutional neural network (1D-CNN) and a collective level of analysis based on behavioral swarm intelligence (BSI). The 1D-CNN captures low-level anomalies at runtime on system calls, network flows, and resource usage, whereas the BSI identifies anomalous interaction patterns among services. A weighted decision fusion scheme is a method that combines the two results aimed at improving the trustworthiness of detection. Cerberus, tested on three datasets including UNSW-NB15, CIC-IDS2017, and a custom Kubernetes-specific (termed as Kube-ZeroDay, KZD-2026) dataset, outperforms LSTM, autoendetraining and graph-based models with an accuracy of 96.8 and a false positive rate of 2.1. The framework also presents a low detection latency (29 ms) and has good behavior with cluster scalability, which demonstrates that it can be applied in practical cloud-native scenario.
Read PDF

Similar papers

Open access Sep 2026

Lightweight AI Models for Cyber Threat Detection: An Evaluation of MobileNetV2, Random Forest, and CNN-LSTM for Phishing and Network Anomaly Detection

This work contributes a comparative evaluation of lightweight detection models, consistent attention to security-critical metrics, and interpretable insights to support practical cybersecurity deployment.

Nwagbara Chisom Telvin, Gilbert Imuetin Osaze Aimufua, Raymond Ternenge Igbudu · 0 citations
Open access 2026

HYBRIDNET-IDS: AN INNOVATIVE CNN, BILSTM, AND TRANSFORMER FRAMEWORK UTILISING ATTENTION FOR IMPROVED NETWORK INTRUSION DETECTION

The rapid spread of network-connected technologies and the growing complexity of attacks have shown that traditional signature-based intrusion detection systems are not good enough, especially when it comes to finding zero-day attacks and advanced persistent threats. This paper introduces HybridNet-IDS, an augmented de...

Subhodip Koley, Sumit Das, Debasish Saha Roy et al. · 0 citations
Conference Aug 2026

An Attention-Driven Hybrid Deep Learning Framework for Intrusion Detection in Cloud-Based E-Learning

E-learning environments on clouds are scalable and flexible, yet are prone to cyberattacks. The current research suggests an Attention-based CNN-BiLSTM Hybrid Intrusion Detection System (ACH-IDS) for the protection of e-learning environment based on clouds from cyberattacks. The system consists of a CNN component for f...

Venkatakrishna Rao Likki, Naga Deepti P, T. Prabhuram et al. · 0 citations
Conference Aug 2026

A Lightweight Hybrid CNN–Gradient Boosting Framework for Real-Time Network Intrusion Detection

Network intrusion detection systems must distinguish malicious from benign traffic under realistic conditions where attack types seen at deployment time may not have appeared during training. This paper presents a lightweight hybrid framework combining a compact one-dimensional convolutional neural network (CNN), used...

S. Satla, M. N. Rao, Tejaswi Katari et al. · 0 citations
Open access Aug 2026

Unsupervised deep learning for IoT botnet detection in a surveillance VLAN via multi-source traffic, threat intelligence and honeypot corroboration

An unsupervised deep-learning detection system using autoencoder (AE)-family models that learn normal traffic behaviors and identify anomalies through reconstruction error (MSE) and provides a transparent, reproducible methodology for proactive, scalable, and interpretable botnet detection.

Özkan Zeybek, Hasan Güler · 0 citations
Open access 2026

A Hybrid Autoencoder and Transformer-Based Framework for Intrusion Detection in IoT Networks

: Intrusion detection in Internet-of-Things (IoT) and enterprise networks must combine high predictive performance with reliable minority-attack recognition, leakage-safe evaluation, and deployable computational cost. This study presents an Optimized Gated Autoencoder-Transformer that preserves standardized raw flow de...

A. Javed, Asim Dilawar Bakhshi, M. M. Alam et al. · 0 citations

Related blog posts

Microsoft Research Blog Jul 13, 2026

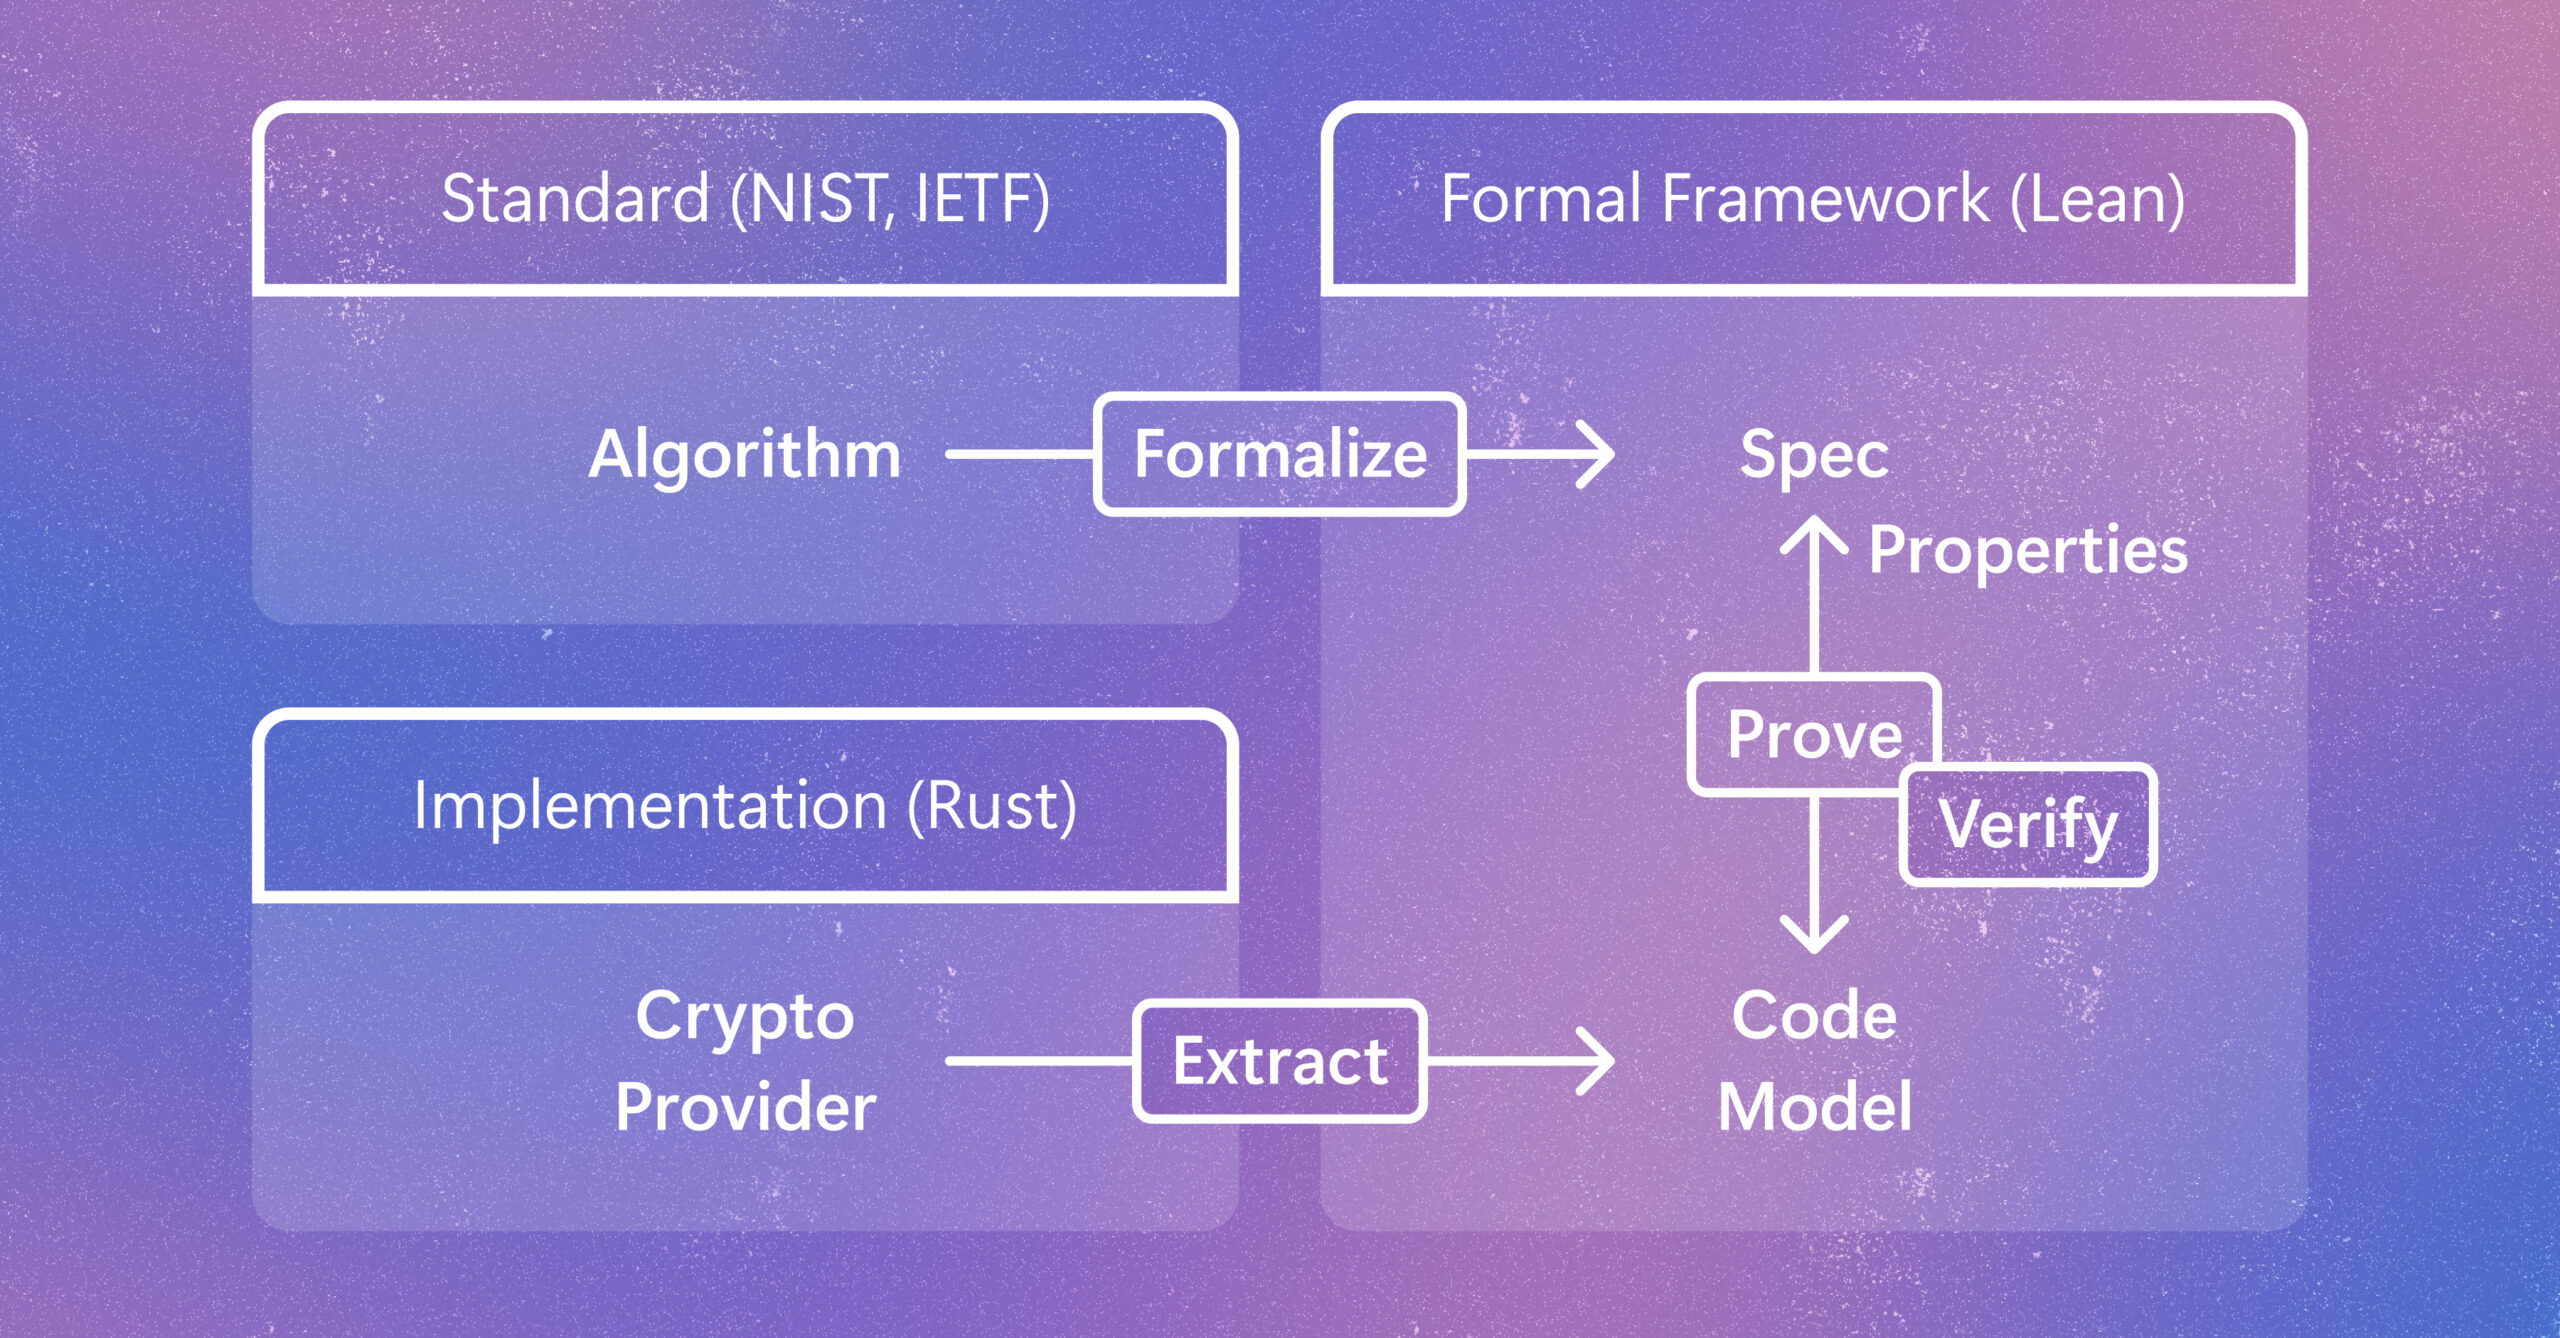
Verifying Rust cryptography in SymCrypt, from standards to code

Cryptographic code supports vital protections in modern computing systems. Learn how a new method helps verify code as developers write it while preserving speed and adaptability as it gets implemented and evolves. The post Verifying Rust cryptography in SymCrypt, from standards to code appeared first on Microsoft Research.

We use cookies to run the site and, with your consent, for analytics and to show ads. See our Cookie Policy.