Open-source package registries such as npm and PyPI are increasingly targeted by software supply-chain attacks in which a trusted package is compromised through a later release. This study reconstructs each candidate release together with its immediate predecessor in npm and PyPI and evaluates machine-learning detection under package-disjoint validation. Against never-compromised controls selected within ecosystem and matched on candidate archive file count, the model reaches ROC-AUC = 0.801 ± 0.006 and nested grouped F1 = 0.792 (95% CI 0.730–0.845). Performance falls to ROC-AUC = 0.551 when the controls are ordinary updates of the same compromised packages. That gap shows that the evaluated features separate compromised packages from clean packages far better than they separate a malicious update from another update of the same package. A strict temporal hold-out returns F1 = 0.310, and training on one registry and testing on the other gives ROC-AUC = 0.498 from npm to PyPI and 0.630 from PyPI to npm. Version context contributes a small incremental signal, but control construction largely determines apparent performance. The approach is therefore presented as a first-stage screening filter, and the results argue for stronger within-package and temporal evaluation.
This publication proposes a definition and a classification of agile software development approaches and analyses ten software development methods that can be characterized as being "agile" against the defined criterion.
P. Abrahamsson, O. Salo, Jussi Ronkainen et al.· arXiv.org· 727 citations· ⚡54
The study shows that agile practices improve both informal and formal communication, but indicates that, in larger development situations involving multiple external stakeholders, a mismatch of adequate communication mechanisms can sometimes even hinder the communication.
M. Pikkarainen, Jukka Haikara, O. Salo et al.· Empirical Software Engineeri...· 401 citations· ⚡48
The results indicate that software engineering work practices are chosen opportunistically, adapted and configured to provide value under the constrains imposed by the startup context.
Nicolò Paternoster, Carmine Giardino, M. Unterkalmsteiner et al.· Information and Software Tec...· 394 citations· ⚡54
The results show that the embedded industry has been able to apply agile methods in its development processes and that the appreciation of the agile methods and their individual practices appears to increase once adopted and applied in practice.
O. Salo, P. Abrahamsson· IET Software· 238 citations· ⚡9
Consequences of happiness and unhappiness that are beneficial and detrimental for developers' mental well-being, the software development process, and the produced artifacts are found.
D. Graziotin, Fabian Fagerholm, Xiaofeng Wang et al.· Journal of Systems and Softw...· 236 citations· ⚡13
The Mobile-D approach is briefly outlined here and the experiences gained from four case studies are discussed, which helped develop an agile development approach for mobile application development.
P. Abrahamsson, Antti Hanhineva, H. Hulkko et al.· Conference on Object-Oriente...· 225 citations· ⚡18
Related blog posts
MIT News · Artificial Intelligence· news.mit.eduOct 22, 2026
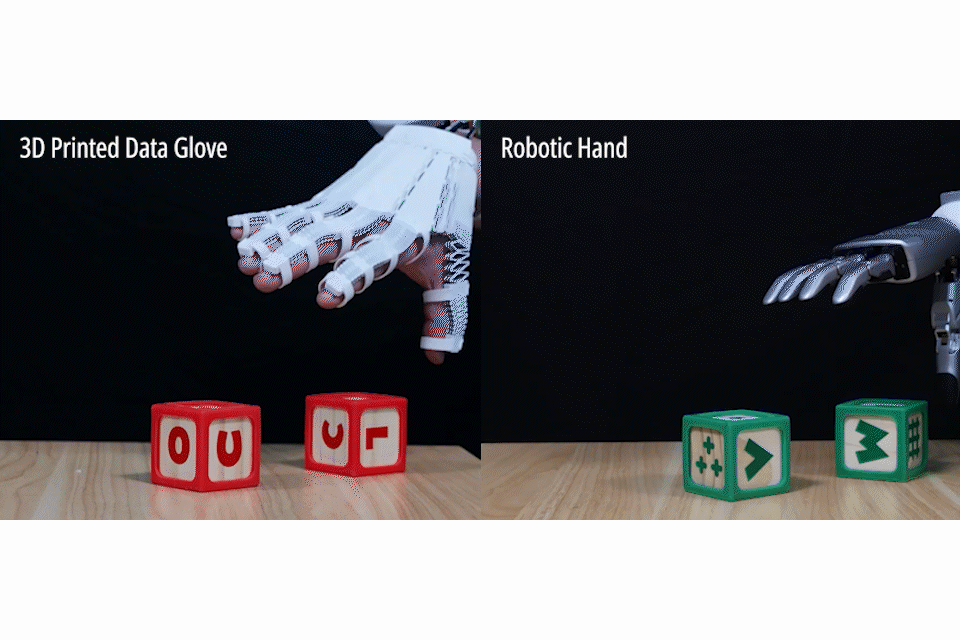
“X-Hinges” helps design and 3D print items like lamps and gloves with an interactive twist: automatically embedded sensors that perceive and adaptively respond to human contact.
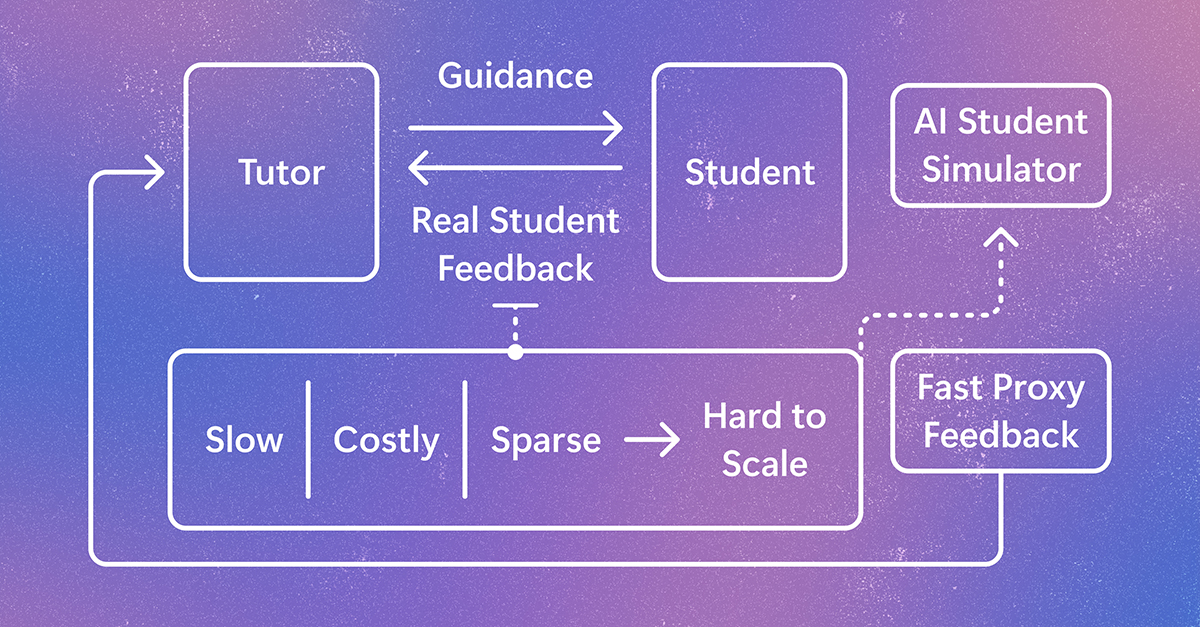
StudentSim is a research system for evaluating and improving AI tutoring tools before they are tested with learners. It models how individuals may engage with tutors, giving feedback to improve tutor performance across subjects like chess, writing, and mathematics. The post Simulating student learning for better AI tutoring appeared first on Microsoft Research.
MIT News · Artificial Intelligence· news.mit.eduOct 6, 2026