Skip to content
#software testing Open access

SSX360/matrixscroll: Matrix Scroll 0.11.0: protocol v2

Oct 2026 · Zenodo (CERN European Organization for Nuclear Research)
Blockchain Technology Applications and Security

Abstract

Matrix Scroll 0.11.0 introduces protocol v2 with mandatory pure, hedged ML-DSA-87 signatures, attached COSE_Sign1 and RFC 8785 canonical JSON. SHA-384 ledgers use RFC 9162 trees and authenticated checkpoint coverage. Python, Rust, Node WebCrypto and the bundled browser verifier share CONSISTENT / INDETERMINATE / INCONSISTENT verdicts. This is a breaking protocol baseline. Generate a fresh v2 identity, explicitly enroll it in your trust policy and start a new v2 ledger. Current interfaces accept v2 only. Preserve historical signatures and use the separately labeled legacy artifact for historical verification. Migration guide Protocol specification Research and source register Randomness diagnostics and limits Software keys use seed-based PKCS#8. Every signing path uses IdentityProvider and verifies its output. Unsupported providers and FIPS custody mode fail closed. MCP exports stay local unless hosted mode is explicit, and raw exports do not claim verification results. Install with python -m pip install "matrixscroll[mcp]==0.11.0" after the Trusted Publishing workflow confirms PyPI availability. The attached offline HTML verifier bundles its dependencies and requires no network. Check its attached SHA-256 file before use. Release source: 7b0d26d61b885686a5d0d0cdd7054882733927e3. Wheel and source archive were built on Linux with Python 3.12.14, build 1.6.1, hatchling 1.32.4 and SOURCE_DATE_EPOCH from that commit. Repeated clean builds produced identical bytes. The digest manifest records exact source and artifact hashes. The publishing workflow rebuilds and compares the artifacts before upload. The maintainer explicitly approved merging and finalization on October 5, 2026. PRs #74 and #77 used the maintainer override, with repository review settings retained. This approval is not an independent GitHub code-owner review. Historical releases and tags remain unchanged. Verification boundaries: a valid signature establishes consistency of supplied bytes, not signer authorization or trusted time. CNSA alignment applies to the ML-DSA-87 signature and SHA-384 ledger algorithm profile, as evidence mapping, not a certification claim. Optional sealed-pack encryption has a separate profile. Module validation, physical resistance, KMS/HSM custody, witnesses and hardware remain outside this release's assurance. Validation on this source: 759 installed-wheel tests and 78 subtests pass, with one expected Rust-wrapper skip in that job. All four verifier backends agree on 10,000 generated documents and 39 fixture/parser cases. The offline browser passes 25 cases with zero HTTP requests. Eight TLC configurations, Rust and JavaScript tests, strict docs, Vale and package validation pass. Some additional GitHub platform jobs remain queued during the October 5 Actions runner incident; the recorded local checks remain distinct from those pending runs.
View source

Similar papers

#computer vision Review Sep 2017

Agile Software Development Methods: Review and Analysis

This publication proposes a definition and a classification of agile software development approaches and analyses ten software development methods that can be characterized as being "agile" against the defined criterion.

P. Abrahamsson, O. Salo, Jussi Ronkainen et al. · 727 citations · ⚡54
#computer vision Jun 2008

The impact of agile practices on communication in software development

The study shows that agile practices improve both informal and formal communication, but indicates that, in larger development situations involving multiple external stakeholders, a mismatch of adequate communication mechanisms can sometimes even hinder the communication.

M. Pikkarainen, Jukka Haikara, O. Salo et al. · 401 citations · ⚡48
#machine learning Review Open access Oct 2014

Software development in startup companies: A systematic mapping study

The results indicate that software engineering work practices are chosen opportunistically, adapted and configured to provide value under the constrains imposed by the startup context.

Nicolò Paternoster, Carmine Giardino, M. Unterkalmsteiner et al. · 394 citations · ⚡54
#computer vision Review Mar 2008

Agile methods in European embedded software development organisations: a survey on the actual use and usefulness of Extreme Programming and Scrum

The results show that the embedded industry has been able to apply agile methods in its development processes and that the appreciation of the agile methods and their individual practices appears to increase once adopted and applied in practice.

O. Salo, P. Abrahamsson · 238 citations · ⚡9
#computer vision Open access Jul 2017

What happens when software developers are (un)happy

Consequences of happiness and unhappiness that are beneficial and detrimental for developers' mental well-being, the software development process, and the produced artifacts are found.

D. Graziotin, Fabian Fagerholm, Xiaofeng Wang et al. · 236 citations · ⚡13
#computer vision Open access Oct 2004

Mobile-D: an agile approach for mobile application development

The Mobile-D approach is briefly outlined here and the experiences gained from four case studies are discussed, which helped develop an agile development approach for mobile application development.

P. Abrahamsson, Antti Hanhineva, H. Hulkko et al. · 225 citations · ⚡18

Related blog posts

Microsoft Research Blog Oct 12, 2026

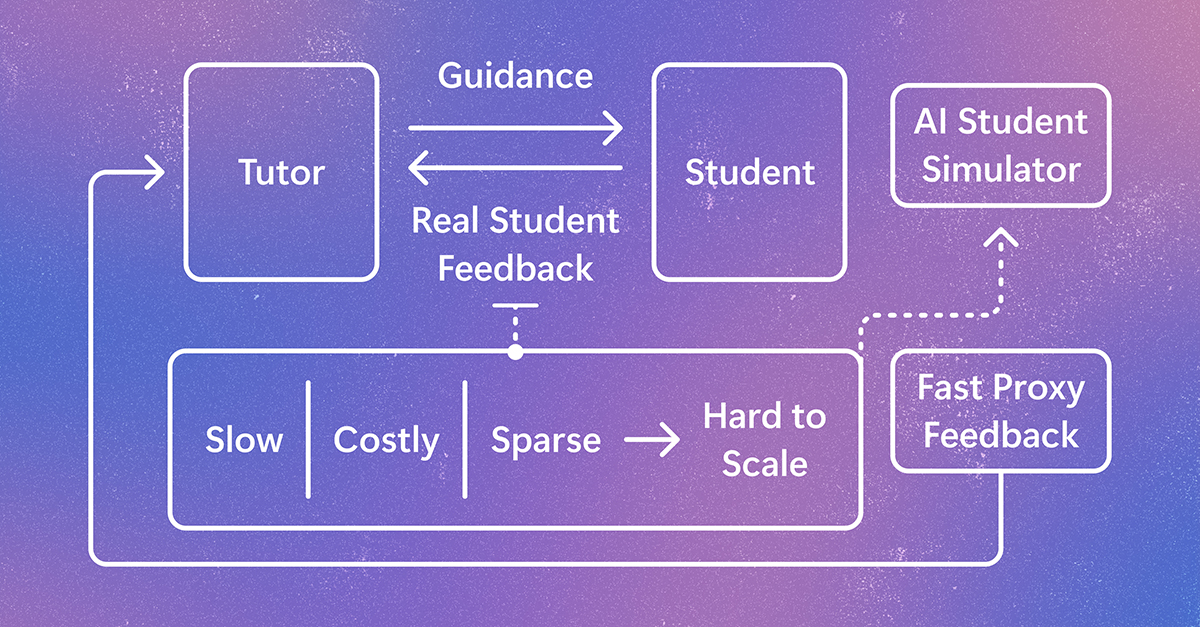
Simulating student learning for better AI tutoring

StudentSim is a research system for evaluating and improving AI tutoring tools before they are tested with learners. It models how individuals may engage with tutors, giving feedback to improve tutor performance across subjects like chess, writing, and mathematics. The post Simulating student learning for better AI tutoring appeared first on Microsoft Research.

We use cookies to run the site and, with your consent, for analytics and to show ads. See our Cookie Policy.